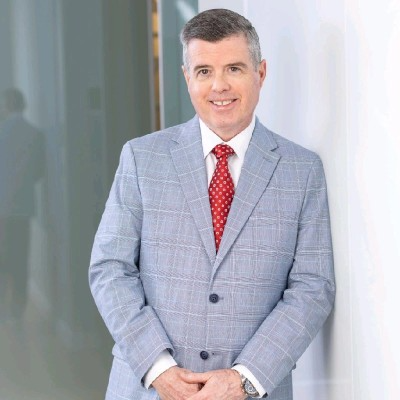
Kevin Mcmahon
Senior Vice President of Audit and Chief Compliance Officer Calpine
Kevin McMahon is responsible for managing and conducting all internal audit activities, NERC, FERC, CFTC Regulatory Compliance, supporting operations and the functional departments as requested, and reporting audit findings with the appropriate recommendations to senior management and the Audit Committee. Prior to joining Calpine, Kevin was Vice President and General Auditor for Exide Technologies, a global manufacturer of stored electrical energy products and services for industrial and transportation applications. He previously served as Vice President-Internal Audit Services and in other senior auditing positions for HCA, Inc., the largest hospital provider in the United States, and served in senior management and auditing positions for Ernst & Young LLP, Southern Company Services, FPL Group and HSBC/Marine Midland Bank N.A. Kevin served on the board of directors of Flotek Industries (NYSE: FTK) and is a past chairman of its audit committee. He has a master of business administration degree from Palm Beach Atlantic University and a bachelor of science degree in accounting from the State University of New York, and is a Certified Internal Auditor.
Day 2 Agenda
9:15 AM PANEL DISCUSSION: ALL HANDS ON DECK: BUILDING THE CYBER INCIDENT RESPONSE PLAYBOOK
When a cyber incident hits, the first hours and days are critical. Legal must move quickly to coordinate the internal response, shape the external narrative and protect the organization's position with regulators, customers and the market. Immediate decisions around investigation scoping, internal escalation, notifications and media engagement can determine the level of trust retained, the scale of litigation and enforcement exposure, and the long-term impact on reputation. A clear response framework that integrates legal, PR, information security and executive leadership is now essential to managing a cyber incident from the moment it is detected.
- Coordinate the response by examining how legal, security, communications, and executive teams align during the critical first hours of cyber incident
- Protect stakeholder trust by exploring how organizations can shape clear, credible communications with regulators, customers, employees, and the wider market
- Strengthen preparedness by identifying the essential playbooks, tools, and decision frameworks needed to respond quickly and consistently
Check out the incredible speaker line-up to see who will be joining Kevin.
Download The Latest AgendaIn Partnership With:

QUESTIONS?
Address: IQPC Ltd, 129 Wilton Road,
London SW1V 1JZ
Telephone: +44 (0) 207 368 9484
Fax: 44 (0) 207 368 9301
Email: exchangeinfo@iqpc.com

©2026 IQPC. All rights reserved.


